Netra Data Protection
One Console, One Policy, Every Exit Path.
Netra protects sensitive data across AI chatbots, embedded AI, SaaS apps, email, cloud storage, screens, peripherals, and endpoints for both employees and AI agents.
Netra Data Protection
Netra protects sensitive data across AI chatbots, embedded AI, SaaS apps, email, cloud storage, screens, peripherals, and endpoints for both employees and AI agents.

Modern data loss rarely looks like a simple file transfer. It happens across endpoints, SaaS apps, AI prompts, screens, personal tools, and human workflows.
Critical IP often leaves in the final weeks before an employee departs, through USB devices, personal cloud storage, email, or unsanctioned apps.
CISO, HR, Legal
Remote-control tools, file-transfer apps, and unmanaged SaaS services can move data through paths that cloud proxies and legacy DLP never see.
SecOps, IT Ops, CISO
A phone pointed at a monitor can capture sensitive data without creating a file movement event for traditional DLP to inspect.
IP owners, R&D
Sensitive data can leave through ChatGPT, Claude, Copilot, coding assistants, and other AI tools as prompts, responses, or agent context.
CISO, AI Governance
The common pattern is the last mile: the endpoint, the SaaS session, the screen, and now the prompt. That is where Netra sits.
No gateway, no proxy, no new hardware — the endpoint agent is already there.
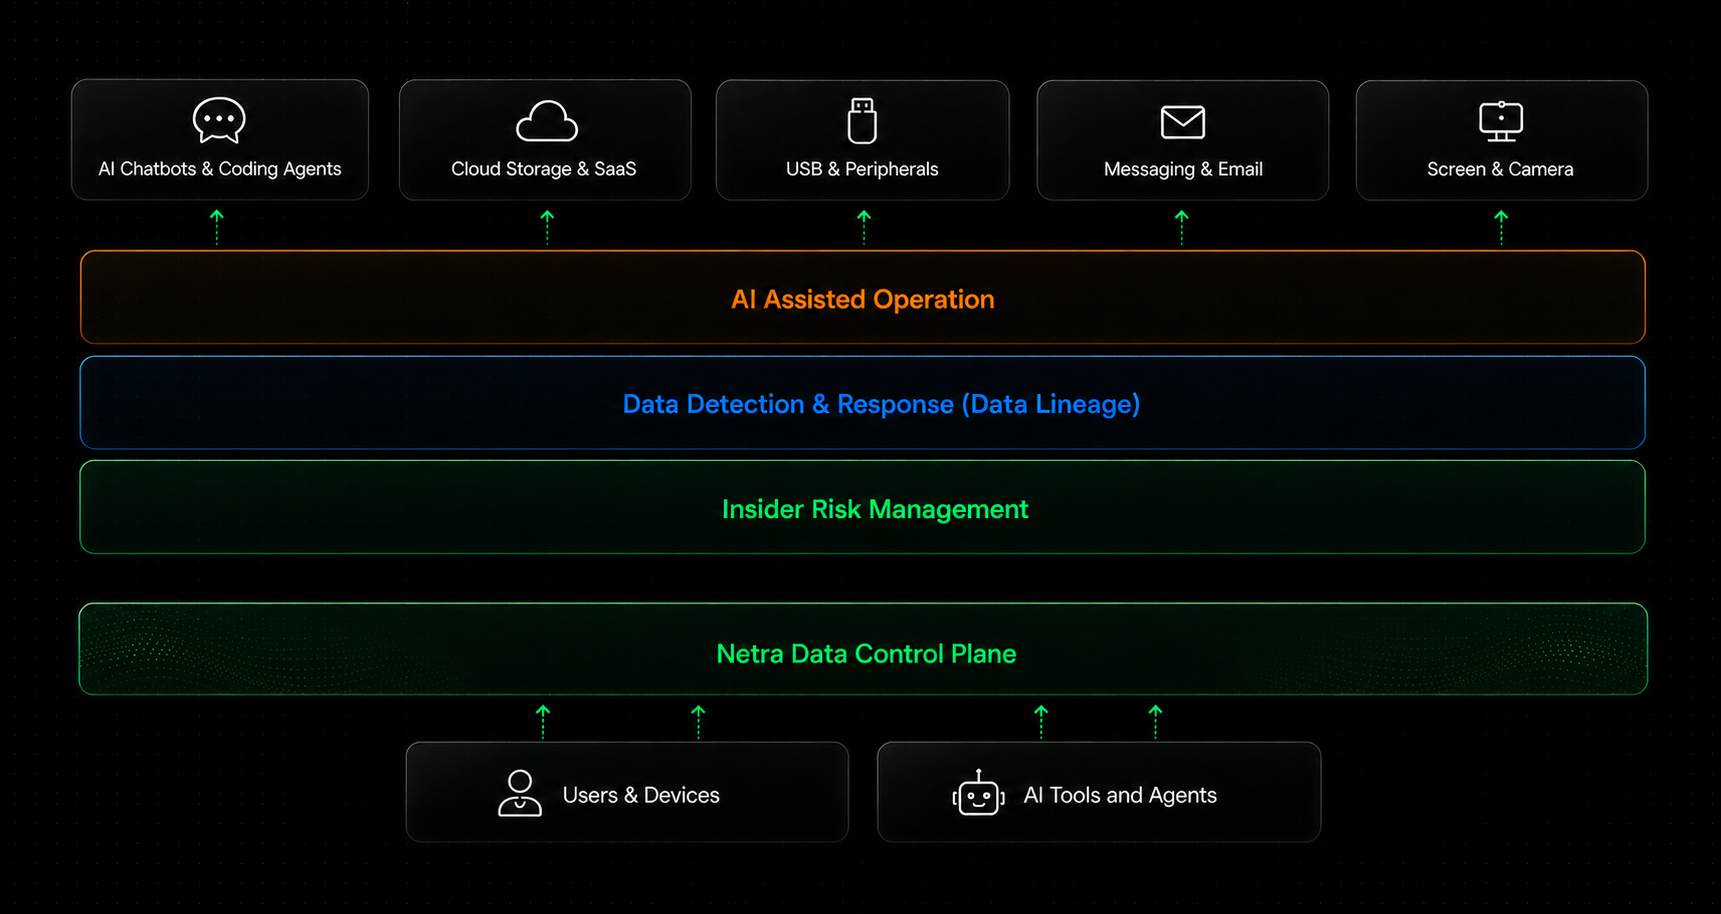
Discover emerging applications, sensitive data, and risky data movement patterns across managed and unmanaged channels. Map sanctioned, unsanctioned, new, and allowed channels before data leaves the organization.

Understand how sensitive data moves across enterprise environments, from source to destination, with context for users, apps, and channels.
Data detection and response starts with full lineage, not isolated alerts.

Detect insider risk in real time using context from endpoints, networks, SaaS apps, AI tools, and user behavior. Identify sensitive data and IP leakage patterns before they become incidents.

Use AI to classify data, analyze events, triage alerts, and reduce false positives at speed and scale.
AI-assisted log analysis and alert triage help teams focus on real risk.

The user, Magic Johnson, demonstrates clear and deliberate intent to exfiltrate sensitive company data by actively seeking ways to bypass DLP controls and transferring confidential business information to a personal Dropbox account.

The user's actions deviate substantially from normal business operations. Transferring sensitive marketing and IPO-related data to personal cloud storage is a clear policy violation and not aligned with the user's role or legitimate business needs.

Immediately suspend the user's access to sensitive data and corporate cloud storage integrations pending a full investigation.
Conduct a thorough forensic analysis of the user's devices and network activity to identify the scope of data exfiltration.
Run a 30-day proof of value on your own data, not a demo environment.
Get a Demo